
Form Guard adds challenge, timing, rate, spam and identity checks to WordPress forms and account screens. It has adapters for ten form plugins and for the Vendix ARN Form widget, and protects the WordPress login, registration and password reset forms. When it is off, it registers no public hooks and loads no files.
Where to find it: ARN Vendix → Form Guard, with the tabs Vendix Form Guard, CAPTCHA Engine, Spam Shield and Identity Guard. Form Guard is part of Vendix Pro and off by default.
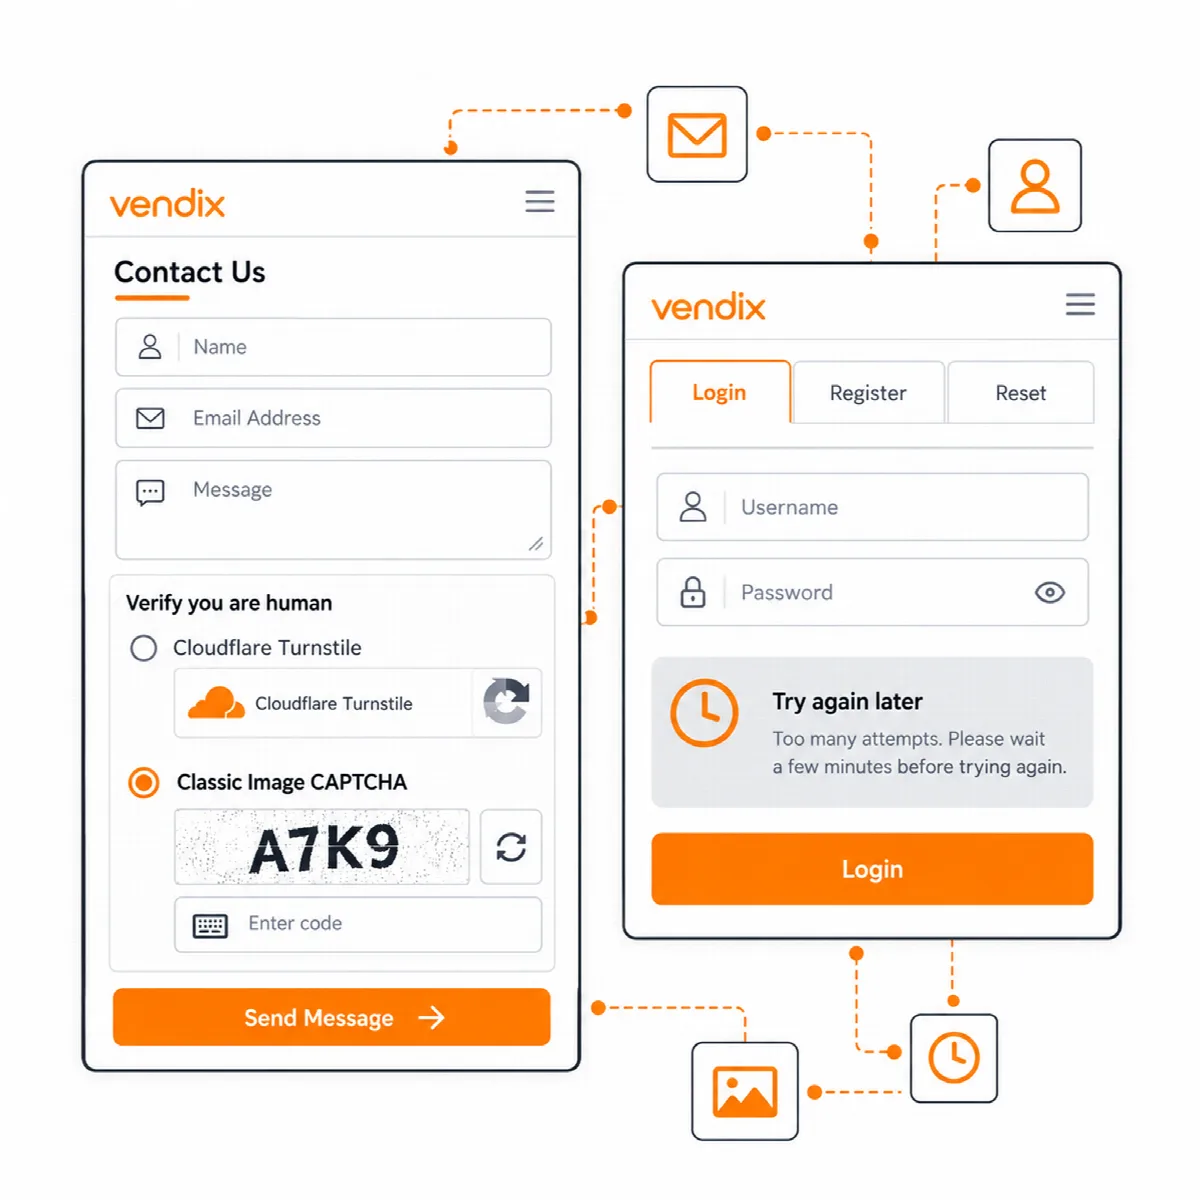
Turn on Form Guard
- Open ARN Vendix → Form Guard and turn on Enable Form Guard.
- Under Protected form systems, check the form plugins you use: Elementor Pro Forms, QuForm, Contact Form 7, WPForms, Gravity Forms, Fluent Forms, Ninja Forms, Forminator, JetFormBuilder and Everest Forms. Each adapter switch starts on and takes effect only when its form plugin is installed.
- Keep Vendix Forms (ARN Form widget) on to protect the ARN Form widget (Vendix 3.0.0 and later). It starts on and needs no other plugin.
- Click Save Vendix Settings.
With the Vendix Forms adapter, the CAPTCHA, the spam score and the blocked terms of Form Guard check each ARN Form message before it is stored or emailed. The form's own spam checks run as well; see Collect messages and sign-ups with ARN Form.
Form email, webhook and CRM actions run only after the server-side check passes. Pages without a protected form load no Form Guard stylesheet, script or Turnstile; a small detector loads them when a protected form appears, also in pop-ups, Full Modal content or forms drawn later by scripts.
Choose the challenge
In the CAPTCHA Engine tab, choose the CAPTCHA type:
- Cloudflare Turnstile Managed — Recommended. Enter your own Turnstile Site key and Secret key. Both can also be defined in
wp-config.php, for example withARN_VENDIX_TURNSTILE_SITE_KEY. Choose the Theme (Auto, Light or Dark) and the Widget size (Normal, Compact or Flexible). The server check also confirms that the answer belongs to your site. - Vendix Classic Image CAPTCHA — Local. A local image code without any third-party service. Set the Code length (4 to 8 characters) and the Challenge expiry. It is meant for standard protection; use Turnstile for high-security sites.
When Turnstile is on, its script loads from Cloudflare and a visitor token and IP address are sent to Cloudflare for verification when a protected form is submitted. From Vendix 3.0.0, Form Guard registers this script under its own name (arnvx-cloudflare-turnstile), so a plugin that registers a script called cloudflare-turnstile with another file cannot change what Form Guard loads.
Tune the spam checks
In the Spam Shield tab, each signal adds to a risk score, and the submission is blocked when the score reaches the Block threshold (40–100):
- Minimum completion time (seconds): a form sent faster than this (1 to 30 seconds) is treated as automated.
- Submissions per client / 10 minutes: the rate limit per client address and form (2 to 100).
- Block duplicate submissions and the Duplicate window (seconds): the same content sent again within the window is caught.
- Enable content risk scoring: too many links (Allowed links per submission), long runs of one repeated character and Blocked terms raise the score. Enter one term or domain per line; matching ignores upper and lower case.
- A hidden honeypot field and a signed start time catch bots that fill in every field or skip the form.
Give normal visitors enough time to fill in the form, and set the rate limit with shared connections in mind. A blocked submission is a policy result, not proof that the sender was malicious.
Protect WordPress accounts
In the Identity Guard tab:
- Turn on Protect WordPress login, registration and password reset. Known and unknown accounts get the same neutral message.
- Optionally turn on Require the selected CAPTCHA on WordPress account forms.
- Set Attempts before cooldown (3 to 30) and the Cooldown (seconds): 300 to 86,400, that is five minutes to 24 hours.
- Optionally turn on Hide unauthenticated WordPress REST user endpoints and Block numeric ?author= user discovery.
- Optionally keep the latest 200 anonymized security events. The log stores only the event type, the risk reasons, the time and a salted client fingerprint; usernames, email addresses, passwords and message content are never stored. Recent blocked events lists them.
These account protections start switched on when you enable Form Guard.
Test after every change
- Send a normal test submission on every protected form and check that the email or other action arrives.
- Send a submission with a wrong or missing challenge and check that it is refused.
- Test the login, registration and password reset screens.
An adapter protects the documented submission path of its form plugin. Custom forms and unusual extensions need their own test.